Compared with generic audits
Elsewhere
A compliance checklist with limited technical validation.
With OffSeq
Testing based on relevant attack paths, supported by evidence of potential business impact.
Evidence-Led Cybersecurity
Penetration testing, red teaming, OT security and NIS2 / DORA readiness for organisations across the EU.We verify security through attacker-led testing, clear evidence and practical remediation guidance.
Reply within 24 hours · Re-testing available for every engagement
OffSeq is an EU-based cybersecurity company working with organisations across Europe, backed by public evidence, international certifications and EU-wide regulatory expertise.
Credited CVEs and coordinated disclosures in software used across Europe and beyond – from national eID systems to enterprise and data-exchange platforms.
Connected to the European Cybersecurity Competence Centre (ECCC) network through its national coordination centres across the EU.
Compliance audits, gap assessments and threat-led testing aligned with the EU requirements relevant to your organisation.
Verified results
The specialists who conduct our client engagements also perform independent vulnerability research and build the tools used in our work. The results below are publicly verifiable.
| Severity | Finding | Advisory | Year |
|---|---|---|---|
| 10.0Critical | Remote code execution in the OZOLS ERP via an abandoned update domainOZOLS (OzolsSQL) for Windows | CVE-2026-22306 (opens in a new tab) | 2026 |
| 7.3High | Remote code execution in Latvia’s national eID signing softwareeParakstītājs 3.0 for Windows (< 1.10.0) | CVE-2026-0392 (opens in a new tab) | 2026 |
| 8.0High | Cross-instance configuration poisoning in X-RoadX-Road Security Server (< 7.8.2) | GHSA-c5gr-pcm6-828r (opens in a new tab) | 2026 |
Qualifications
Credentials held by the OffSeq team, examined and issued by the standards bodies, defence academies and training providers behind them.
Lead Pen Test Professional
ISO/IEC 27001 Senior Lead Auditor
Google Cybersecurity Certificate

Clarified Security (opens in a new tab)

NATO CCDCOE (opens in a new tab)

How we work
A transparent, repeatable process that turns an attacker’s view of your organisation into measurable security improvements.
Map the attack surface relevant to your organisation, including assets, exposure, people and third parties.
Assess and test through vulnerability analysis, penetration testing, social engineering and red team simulation.
Severity-rated findings with business impact, proof, and a prioritised remediation roadmap.
Continuous monitoring, incident-response readiness and compliance – so gains hold over time.
We combine manual attacker-led testing with reproducible evidence and practical remediation guidance.
Elsewhere
With OffSeq
Elsewhere
A compliance checklist with limited technical validation.
With OffSeq
Testing based on relevant attack paths, supported by evidence of potential business impact.
Elsewhere
Large volumes of unverified results that your team must triage.
With OffSeq
Manual validation by qualified specialists, focused on findings that materially affect risk.
Elsewhere
A report from a provider whose qualifications may be difficult to verify.
With OffSeq
An EU-based team whose work is verifiable in the public record, operating under NDA and offering re-testing to verify remediation.
Create a scoped brief in one minute
Map your posture and get an indicative retainer
Check whether the regulations apply to your organisation
Assess your organisation across six domains
A complete sample report with evidence-backed findings from Critical to Low, CVSS scoring, OWASP mapping and a prioritised remediation plan.
CERT.LV recorded 757,286 compromised devices in Latvian cyberspace in Q1 2026, the highest figure reported to date. Most were classified as configuration weaknesses. This briefing turns the published trends into six practical priorities for the quarter.
Choose the group that matches your situation – from security testing to monitoring, governance, EU regulatory readiness and critical infrastructure.
All servicesPlatform
OffSeq operates its own security platform. The same threat data and tools used in client engagements are also available directly to customers.
Threat intelligence – Vulnerability intelligence prioritised by relevance.
Honeypot intelligence – Real-time intelligence from honeypot telemetry.
Device posture – Endpoint posture and device control, hosted in the EU.
Dark web – Credential-exposure monitoring for your domains.
Web security – Web-exposure analysis with daily change monitoring.
Privacy utility – Browser-based encryption and steganography.
Security Awareness Lab
Enter a 3D office and respond to a phishing email, scam call or AI prompt-injection attempt. Choose a simulation and test your judgment.
In the field
Engagements, venues and equipment – from classified cyber ranges to security-community events.
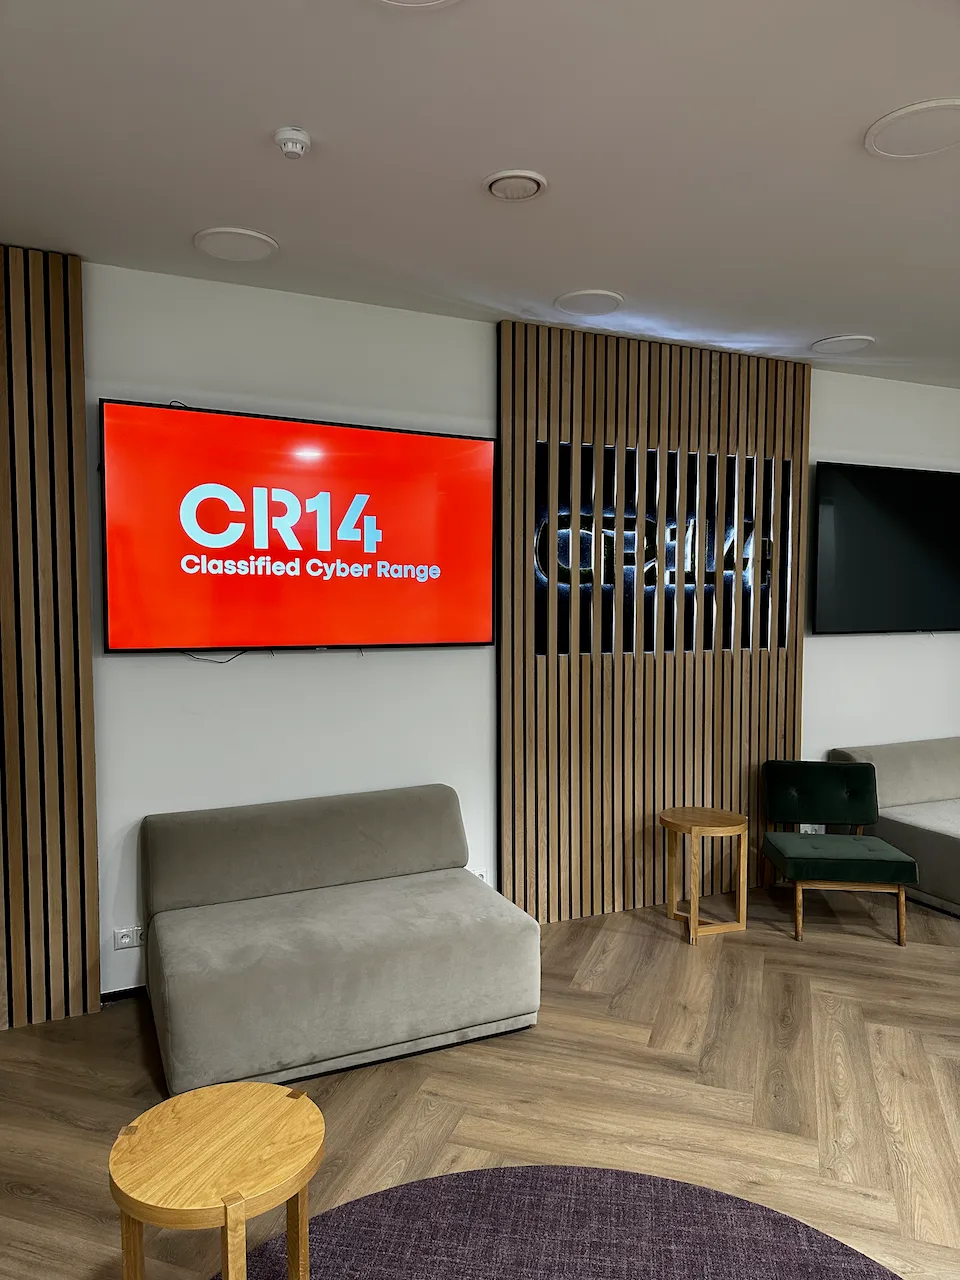
CR14 – classified cyber range
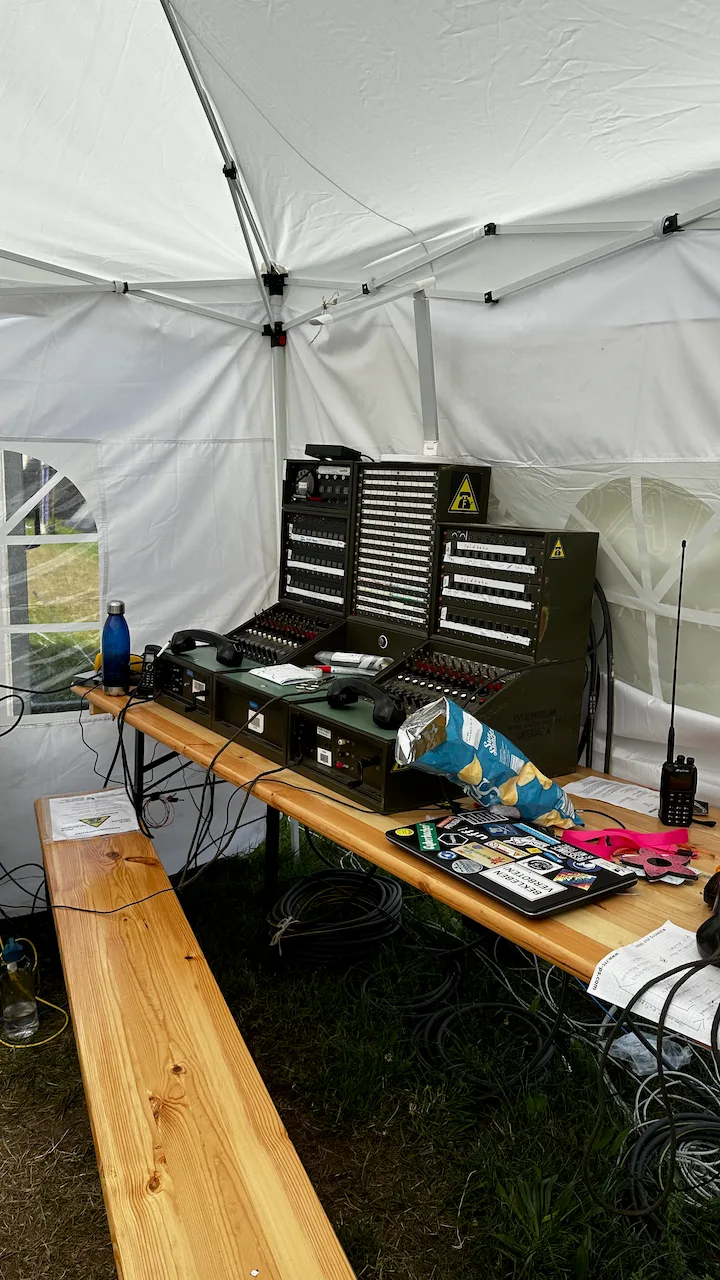
Field kit – hands-on hardware testing
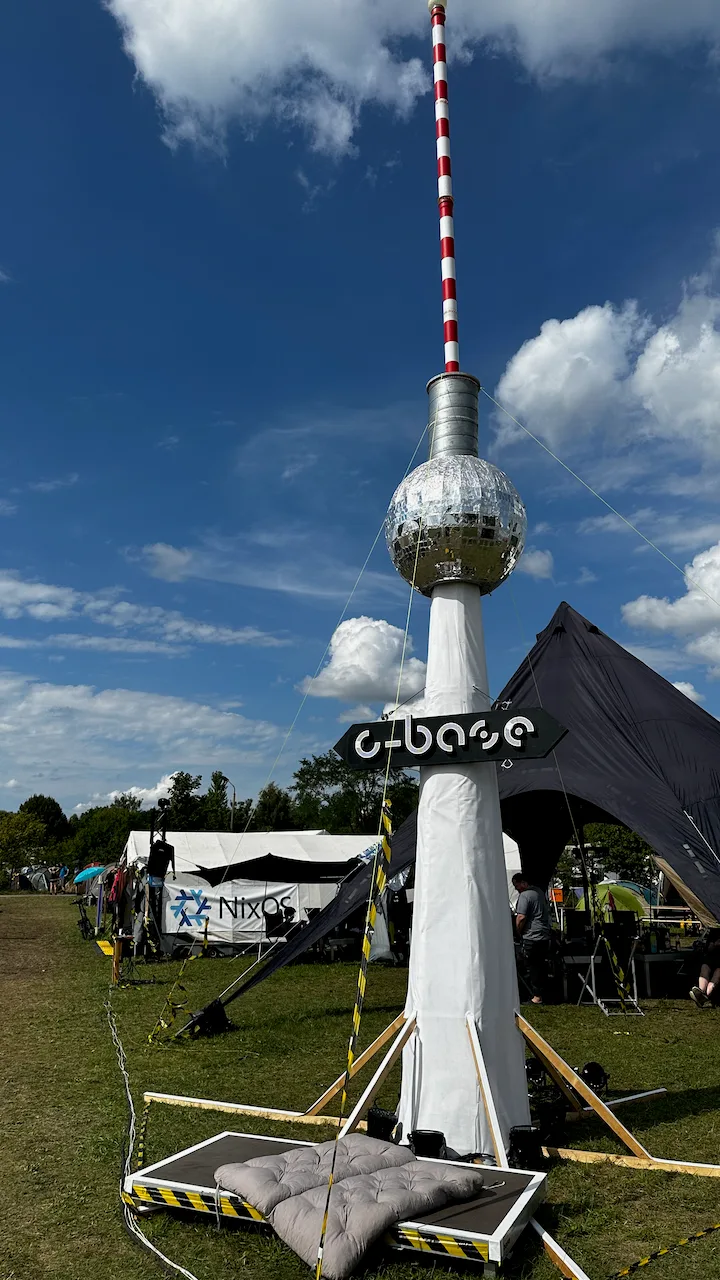
Hacker camps & the security community
At Trace.Space, security has always been a core priority – not an afterthought. As an AI platform trusted by engineering teams building regulated products in automotive, aerospace, medical and defense industries, we hold ourselves to the highest standards. Because we are shipping features at an incredible pace, we recognized that we needed a security partner capable of scaling at our velocity. That is exactly why we partner with OffSeq. We don’t want a standard checkbox compliance vendor; we want an elite partner to help us continuously take our security posture to the next level. Instead of slowing us down, they seamlessly integrate with our fast-moving engineering team, providing proactive, high-level insights that let us fortify our systems in real time as we grow. Working with OffSeq consistently proves that when you are building fast, having a world-class security partner in your corner is the best way to stay ahead of the curve.
In Eleving Group security resilience is at the core of what we do across 17 markets and more than 1.8M customers. Partnering with OffSeq on a red team engagement gave us a genuine adversarial perspective that went well beyond a traditional penetration test. Their team demonstrated deep technical expertise, operated with realism and precision, and communicated findings in a way that was both clear and actionable. We came away more resilient and better informed.
We’ve had the pleasure of working with SEQ SIA (led by Nils Putniņš) on multiple information security engagements at Printful, ranging from targeted penetration testing to in-depth evaluations of our platform’s security maturity. In every project, SEQ SIA has demonstrated a rare combination of technical precision, strategic thinking, and professionalism. Most recently, during a performance and security audit of one of our core systems – used daily by thousands of employees and clients – SEQ SIA delivered beyond expectations. Their structured methodology, clear communication, and actionable insights directly contributed to increased system reliability, scalability, and resilience. SEQ SIA has become a trusted security partner, and we highly value the clarity and confidence they bring to complex security challenges.
Working with OffSeq has been a solid experience from day one. They’ve helped us with red teaming, penetration testing, and assessments – not just for our own systems but also for some of our clients. What stands out is their practical approach – no fluff, just clear findings and actionable recommendations. They know how to dig deep, but they also understand how to communicate technical risks in a way that makes sense to different stakeholders. We’ve come to trust them as a reliable extension of our security team, and we’re looking forward to continuing the collaboration.
I had some expectations when we signed up with OffSeq. I was expecting some social engineering, routine web works to see our loopholes. Instead, they dug with passion, and they dug deep. They found holes me and my IT team were astonished to hear about. They worked from the heart and in high quality.
We export to over 20 countries, so the security of our systems and client data isn’t something we take lightly. OffSeq ran a black-box audit that showed us exactly where we stood – no sugarcoating, just an honest picture from a real attacker’s perspective. The report worked for both our IT team and our board, which is rare. Really solid work all around.
We confirm that SIA “SEQ” conducted three information system security audits in 2025. The audits were carried out professionally and in full compliance with the contractual requirements. We are satisfied with the service provided. – State Emergency Medical Service of the Republic of Latvia (NMPD).
We were working with SEQ and their expert Nils Putniņš for security testing of our systems and we are happy with the results and their fast response time. We recommend SEQ and are looking forward to a long-term collaboration.
Ar šo apliecinām, ka SIA “Codex” ir veiksmīgi sadarbojies ar SIA “SEQ” un tā speciālistu Nilu Putniņu vairāku nozīmīgu projektu ietvaros. Sadarbības laikā esam augsti novērtējuši SIA “SEQ” sniegto pakalpojumu kvalitāti, profesionalitāti un atbildīgo pieeju. Visas saistības veiktas norunātajos termiņos un augstā kvalitātē. Nils Putniņš ir apliecinājis sevi kā augstas klases ekspertu informācijas sistēmu drošības un kiberdrošības jomā.
SEQ and specialist Nils Putniņš performed a security audit for a project in development at Jāņa Sēta in June 2023. We are very satisfied with the test results, which helped improve the system’s security. The work was done quickly and to a high standard. We plan to keep working with SEQ.
The OffSeq team collaborated with the LG team to identify and resolve several high-severity vulnerabilities within LG’s products and services promptly. We appreciate their dedication to helping us improve the security of LG Electronics.
Credentials, proof of work, reporting speed and EU regulation – what buyers ask before signing.
OffSeq is an EU-based cybersecurity company working with organisations across Europe. Our credentials are public: credited CVEs and coordinated vulnerability disclosures; OSCP, OSEP, OSWE, GIAC GXPN, CISSP, CISA and PECB ISO/IEC 27001 Senior Lead Auditor certifications held by the specialists who perform the work; and testing aligned with EU regulation such as NIS2, DORA and GDPR.
Tell us what you need to protect. We will explain how we would test it and how to strengthen its defences. We reply within 24 hours.
Direct access to a senior specialist · Reply within 24 hours · NDA available on request