We think like attackers – for defenders
OffSeq is a European offensive-security company. We help organisations across the Baltics, Scandinavia and the wider EU improve digital resilience by testing defences from an attacker’s perspective.
OffSeq – short for Offensive Sequence – was founded in 2022 on a simple principle: you cannot reliably defend a system that has never been tested from an attacker’s perspective. Every engagement begins by identifying the paths an adversary could actually use.
We combine deep offensive-security expertise with the regulatory requirements European organisations face. NIS2, DORA and GDPR shape how we test, report and advise.
In 2026, OffSeq became a PECB, opens in a new tab training partner, expanding our work into internationally recognised ISO and cybersecurity training and certification, opens in a new tab across Latvia and the EU.
| Founded | 2022 |
|---|---|
| Core services | 33 |
| In-house security platforms | 6 |
Principles we operate by
- 01
Attacker-led
We start with the attack paths most relevant to your environment, not a generic checklist.
- 02
Clear communication
Clear findings and candid advice, without fear-based selling or unnecessary jargon.
- 03
Evidence over opinion
Every conclusion is supported by evidence, a severity rating and an assessment of business impact.
- 04
Built for Europe
Our work reflects the regulatory and operational context of European organisations.
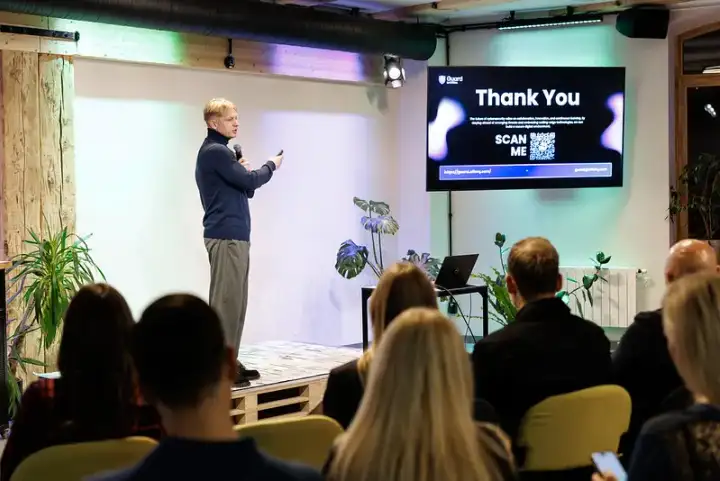
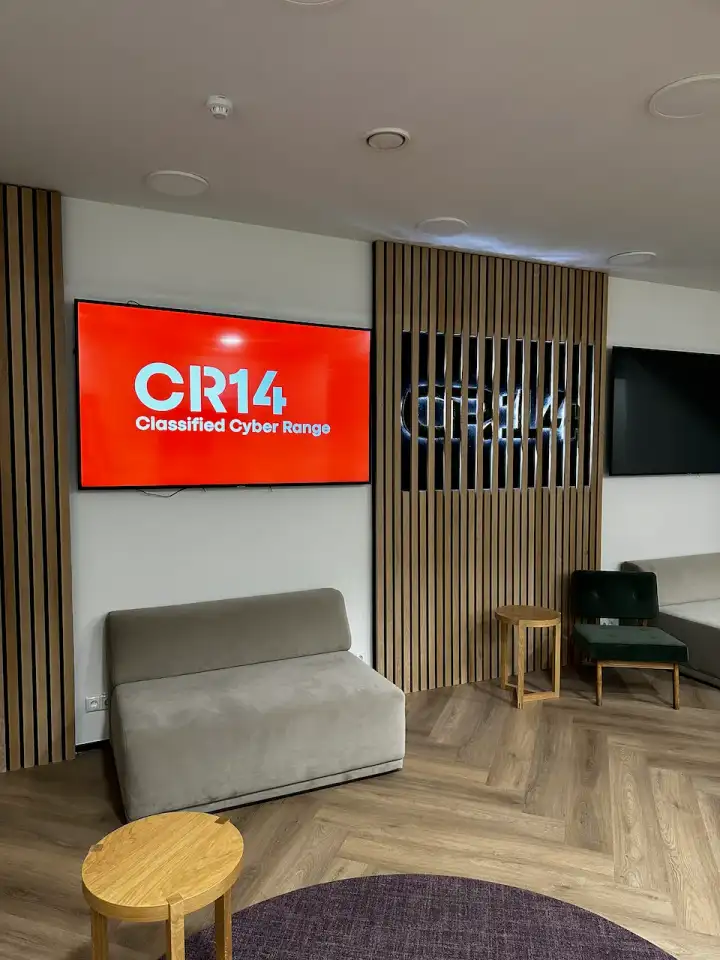
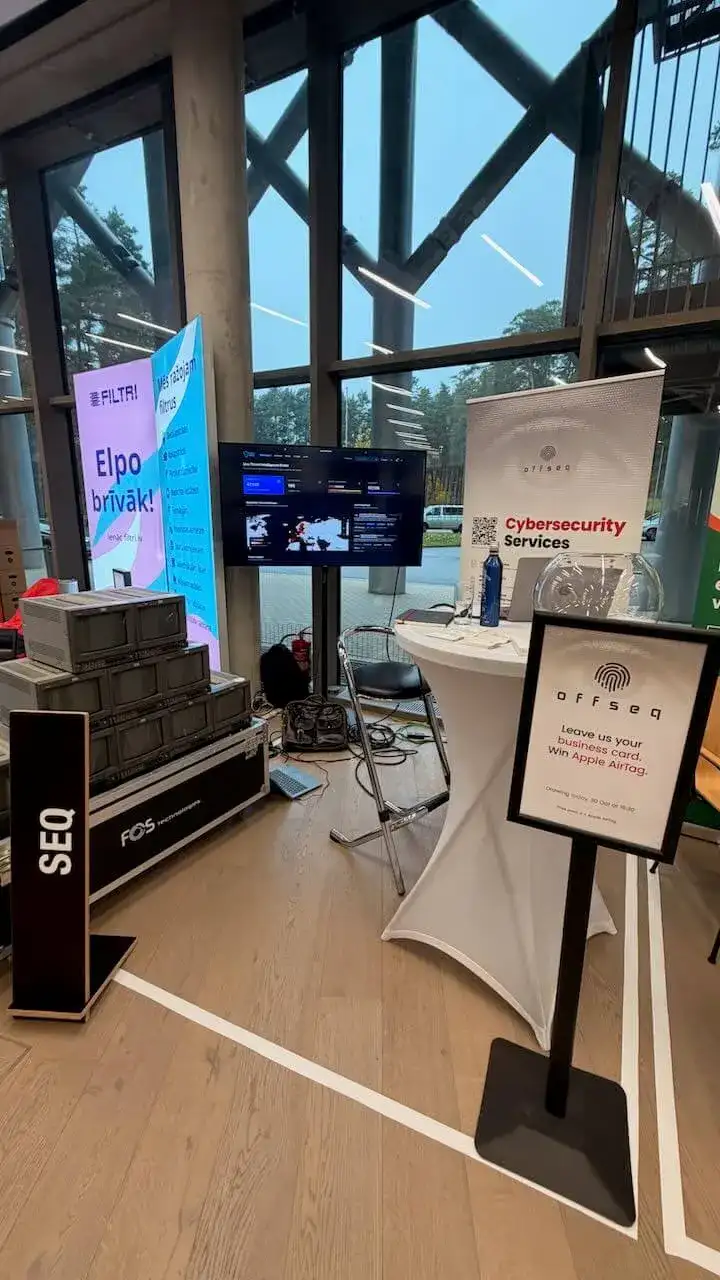
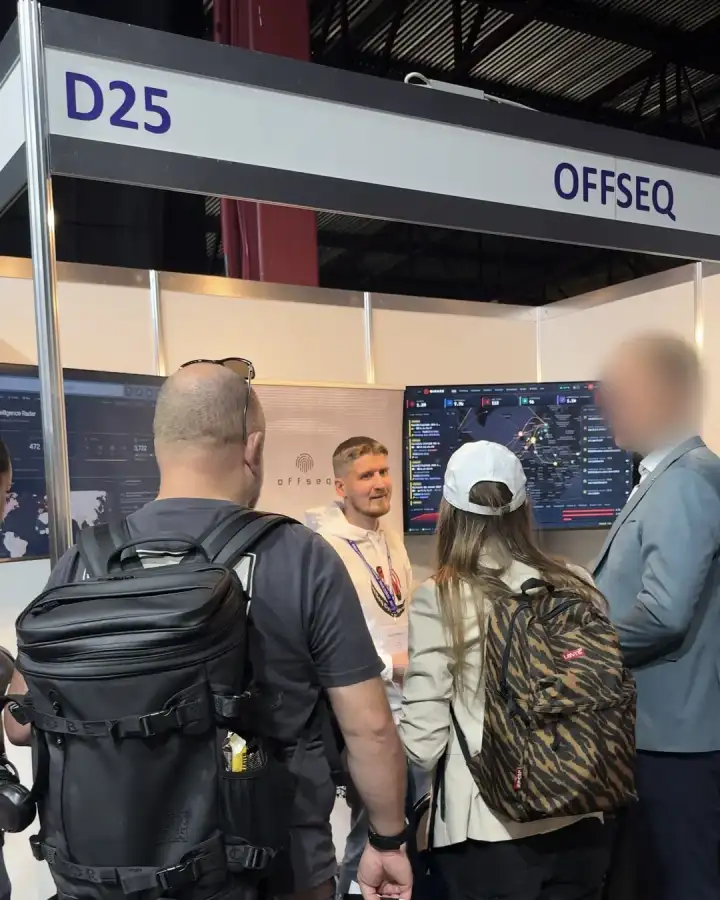
On the ground
Qualifications
Certified to international standards
Credentials held by the OffSeq team, examined and issued by the standards bodies, defence academies and training providers behind them.
Lead Pen Test Professional
ISO/IEC 27001 Senior Lead Auditor
Google Cybersecurity Certificate

Clarified Security (opens in a new tab)
- Red Team Operations
NATO CCDCOE (opens in a new tab)
- Critical Information Infrastructure Protection
- Web Applications Attack & Defence
- IT Systems Attack & Defense
- Cybercrime
- Cyber Bite: Darkweb
- OSINT – Cryptocurrencies
- Security Awareness: Privileged Accounts
Organisations and networks
Selected clients
We build the tools we use.
Selected offensive-security tools used in our engagements are available to the community as open-source projects on GitHub.
github.com/offseq- 01
threat-finder (View on GitHub)
Runtime CVE scanner – finds vulnerabilities in the services actually running on a host, ranked by network exposure.
Rust - 02
php2shell-poc (View on GitHub)
Non-destructive PHP2Shell (CVE-2026-109618/109619) reachability check and offset tooling for authorized testing.
Python - 03
threadsrecon (View on GitHub)
OSINT tooling for Threads (threads.net) – profiles, posts and connections.
Python - 04
rockyou-lv (View on GitHub)
Latvian-language password wordlist for cracking and credential audits.
Python - 05
servicediscovery (View on GitHub)
CIDR-aware Nmap scanner – one process per IP, per-host XML output.
Python - 06
xcompare (View on GitHub)
Find mutual followers between two X accounts without the official API.
Python - 07
homebrew-tap (View on GitHub)
Homebrew tap distributing the OffSeq toolset.
Ruby
EU funding
Strengthening cybersecurity awareness and resilience in Europe
OffSeq participates in EU-funded initiatives that strengthen cybersecurity awareness and resilience by identifying vulnerabilities from an attacker’s perspective and developing proactive monitoring solutions.
Agreement ID: KD/1/24/A/004
Work with a team that tests from an attacker’s perspective
Tell us what you need to protect. We will explain how we would test it and how to strengthen its defences.